
If you private through links in our articles, shall we assemble a microscopic commission. This would no longer have an effect on our editorial independence.

The children believe it lovely. Wired earbuds proof in opposition to the Bluetooth security flaws that protect making wi-fi audio scrutinize so a lot less helpful.
I rob it abet. I change into detestable to scoff on the children.
A pair of months ago, an article crossed my feeds about wired earbuds. In step with my juniors, this retro tech represents elegancy and ease—a greater time.
I change into before the complete lot appalled on the characterization. Having lived through tangled wires and a few snapped cords, I know exactly how Bluetooth headphone dominance got here about. Nonetheless after but one other affirmation of a security vulnerability in a wi-fi audio instrument, I’ve been rethinking my procedure.
Welcome to Get Mode, your weekly file for urgent security and privacy files—and what steps to rob next. Need this text to reach abet straight to your inbox? Sign in on our web field!
This particular enlighten contains Skullcandy’s Dime 3 earbuds. In step with Carnegie Mellon College’s cybersecurity response team (CERT), these wi-fi earbuds will accept pairing requests without client verification. Any nearby, unpaired gadgets can link with the Dime 3 to file audio enter from the microphones, rob over audio playback, trade the earbuds’ audio profile, or disrupt the client’s connection. If attacked, of us that hang Skullcandy Dime 3 buds might per chance well hear an audio alert of a brand contemporary instrument being paired, however might per chance well no longer acknowledge the significance of the notification.
Skullcandy is no longer uncommon in being liable to such a flaw—this files follows on the heels of Apple’s Beats Studio Buds and Inventive’s Sound Blaster Katana V2X soundbar additionally falling prey to audio hijacking over Bluetooth. Nonetheless Skullcandy Dime 3 house owners might per chance well no longer believe receive admission to to a fix. If your pair has older firmware, it remains exploitable. Skullcandy has but to enable a methodology to alter the buds’ interior instrument, so that the safety patch is applied.
I’m likely no longer in coming near wretchedness of being hacked through Bluetooth headphones, however I’m aware of how linked gadgets can encourage as entryways to juicier knowledge. I don’t favor any individual to hear in my calls, let’s have in mind.
The finest resolution is to alter to tech that might per chance’t be as without wretchedness hacked. Going frail-college at the moment looks the smarter formula to cross from a cybersecurity standpoint, and in this case, that’s deciding on wired gadgets over wi-fi. (I’m reminded, as a nerd of a particular classic, of the cell phone machine in Battlestar Galactica.)
Earlier than, taking this stance would believe painted me as an antiquarian (and even a Luddite). Nonetheless the children, of their knowledge, believe as an different made it a orderly pattern. They in actual fact are going to be all lovely.
Within the guidelines
The arena is changing into less and never more non-public—and in some ways, less safe by extension. Flock cameras were discovered to rob intensive photos of passing autos, OpenAI lets other of us gaze extra of your chat prompts than you can additionally inform, and Anthropic needs to examine your financial habits. Every enlighten sounds innocuous on the surface, however the guidelines shared can display worthy extra of your lifestyles than you’d favor.
Swello / Unsplash
The bearing on:
- Ever wonder what lives on a Flock digicam? Hackers did and ended up discovering roughly 1.6 million photography of autos, taken over a three-week length. The cam additionally had instrument in a position to detecting of us, though no facial recognition took field on the digicam. (On the different hand, this discovery does no longer prevent such actions going down after photos add to a central server.)
- Diverse of us might per chance additionally be reading your ChatGPT prompts, in conserving with 404 Media. Known as “Mission Lily,” the initiative has americans comprise in mind the chatbot’s responses to prompts. As a outcome, any sensitive knowledge linked to your health, funds, and additional would be viewed by strangers. Be cautious about what you fragment.
- Anthropic now supports dispute links to financial institution accounts from interior Claude. Known as “Claude Cash,” it’s a long way the latest company to present financial prognosis as an AI chatbot characteristic. (OpenAI additionally lets in you to link financial accounts to ChatGPT.) On condition that chatbot transcripts might per chance well no longer be as non-public as one would hope (gaze above), I expose warning in embracing this characteristic.
The contaminated:
- Hackers protect inserting frail assault study how to work. This time, malicious JavaScript is abet, placing in browser extensions in Chrome and Edge without client approval. If infected, customers can leak credentials, plunge sufferer to meddler-in-the-center attacks, believe their activity screenshotted, and additional. To supply protection to your self, don’t manually commence JavaScript files.
Tip of the week
Alaina Yee / Foundry
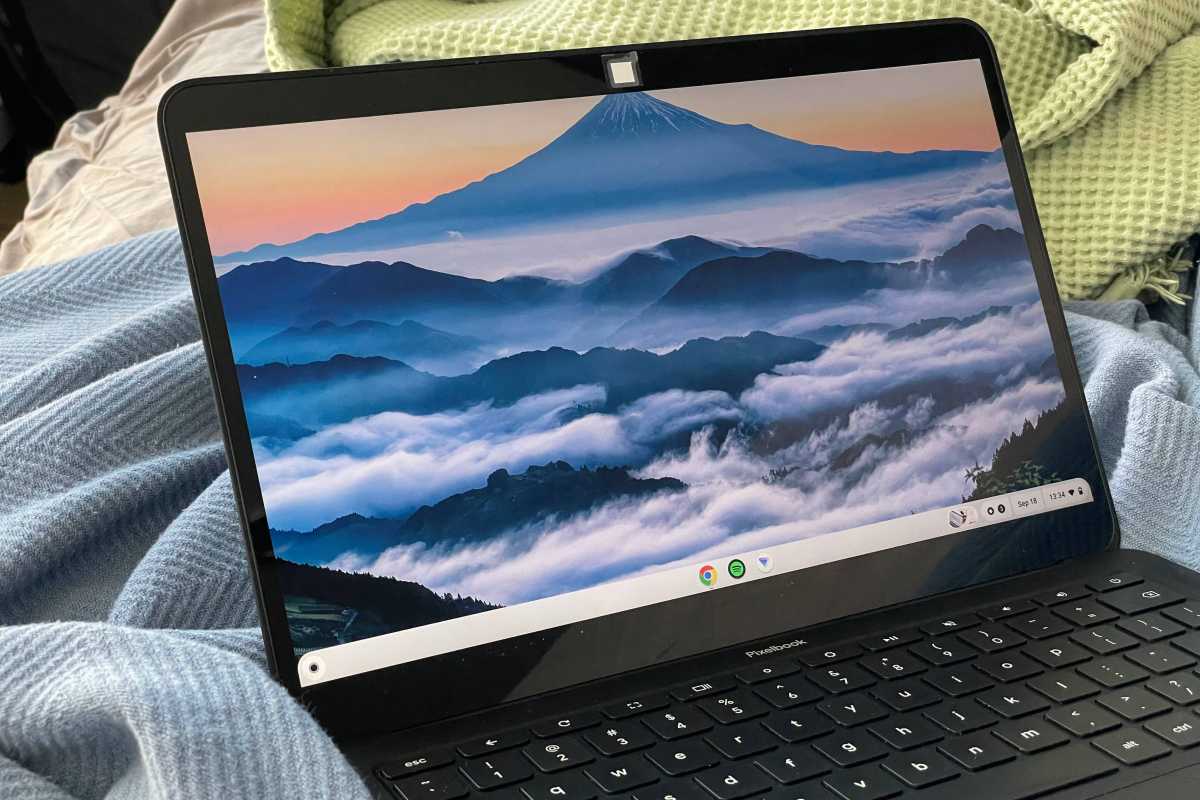
Talking of low tech solutions to excessive tech complications—are you terrified about any individual spying on you via your webcam? You might per chance receive abet some peace of mind by actually retaining the digicam for your gadgets.
You might per chance purchase particular covers on Amazon and other storefronts for this, however I on the total upright cut a microscopic sq. from the sticky share of a Put up-It. You might per chance say and receive greater the digicam extra without wretchedness. If I don’t inform I’ll ever use an embedded webcam in a notebook computer, I’ll use quite of paper and tape.
Demonstrate that this won’t resolve the underlying trigger of being spied on. Drag a scan of your machine with antivirus instrument, and additionally test for any unknown apps or browser extensions.


